

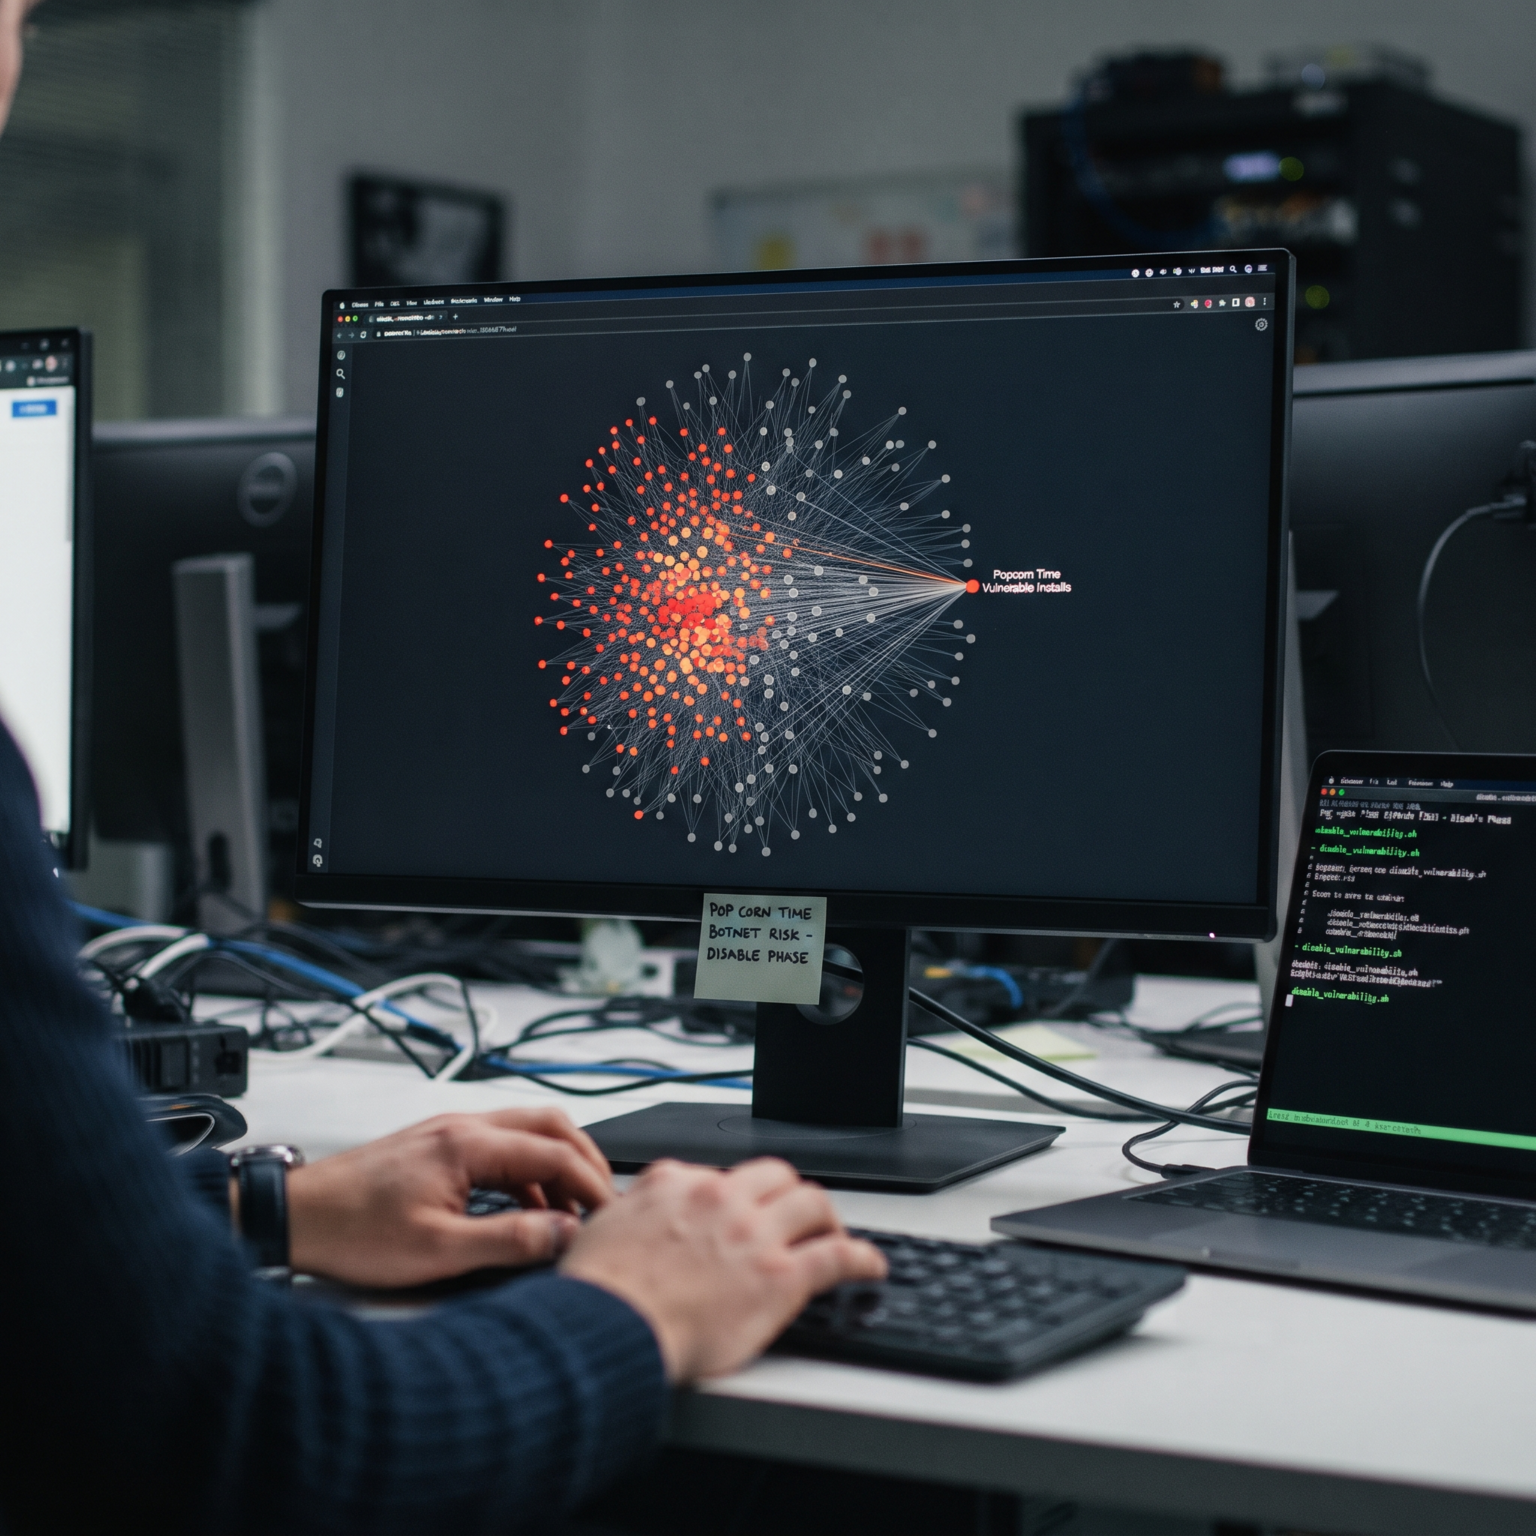
An abandoned app can remain dangerous long after its creators walk away, because software installed on a device does not disappear when development stops; Popcorn Time’s dormant footprint shows how yesterday’s convenience can become tomorrow’s security problem for millions. The streaming application, once widely used to watch films and television, had been discontinued years earlier, yet millions of copies reportedly remained installed, creating an unexpectedly large population of devices running software no longer maintained by its original developers. Although the project was dormant, the installed software still represented an attack surface: if weaknesses could be exploited, compromised devices might be directed remotely, without their owners realizing that an old entertainment app had become an instrument of someone else’s operation. The apps had to be disabled to prevent attackers from turning that lingering user base into a botnet, a network of infected machines that can be controlled together.
The precise route from an abandoned application to a recruitable device is not detailed in the available account, so the episode should not be mistaken for proof that every installation was compromised. Its warning is nonetheless clear: software that no longer receives security fixes can become a liability, especially when it persists across many devices and users have little reason to check whether it is still supported. Attackers seek such opportunities because a single flaw, when present across a broad population, can offer leverage far beyond the value of any one machine. Disabling the applications was therefore a defensive measure aimed at closing a door before dormant installations could be converted into active infrastructure.
A botnet is not simply a collection of hacked computers; it is a distributed tool that lets an operator coordinate many devices from a distance. Depending on the circumstances, such networks can overwhelm websites with traffic, relay spam, conceal malicious activity, or support other attacks, while the owners experience slowdowns, unusual data use, or no obvious symptoms at all. The appeal to criminals is scale: hundreds of thousands of ordinary machines can generate substantial combined capacity without requiring attackers to own expensive servers. That makes the Popcorn Time episode relevant beyond streaming software, because everyday connected devices can become resources in conflicts their owners never chose.
The case also exposes a mismatch between how people think about apps and how software actually behaves. Consumers often treat installation as a one-time decision, but applications may retain permissions, background services, network access, or outdated components long after their original purpose fades. A forgotten app can therefore sit outside the routines that users apply to actively maintained products, leaving it less likely to receive scrutiny or updates. The practical lesson is not to panic over every old program, but to periodically review installed software, remove what is no longer needed, and favor products whose makers communicate clearly about support and security.
For developers and distributors, the story raises a harder question: what responsibility remains when a product reaches end of life? Ending development does not automatically remove software from users’ devices, and a shutdown announcement may be missed by people who installed an app years before. Companies can reduce risk by publishing clear retirement notices, explaining the steps users should take, and, where technically and legally feasible, disabling unsafe functionality or directing users to a safe removal process. App stores and operating-system vendors also influence the lifecycle through support policies, permission controls, warnings, and tools that help identify software that has stopped receiving updates.
The broader market is moving toward a model in which software security is treated as a continuing service rather than a feature delivered at launch. That shift is visible in phones, smart televisions, routers, and connected home products, where devices may outlast the period during which a vendor provides patches. When support ends, consumers can face a difficult choice between replacing hardware, accepting risk, or limiting how the device connects to the internet. Businesses face similar concerns at greater scale: unmanaged software across employee devices can create entry points that are difficult to inventory and costly to contain.
Popcorn Time’s lingering installations illustrate why cybersecurity depends on lifecycle management as much as on defending against the latest attack. A product can be popular, useful, and apparently harmless, yet become dangerous when maintenance ends and its user base remains exposed. Disabling the apps may prevent one particular route to a botnet, but it does not solve the wider challenge of tracking abandoned software across a digital world built on long-lived devices. For users, the durable response is straightforward: keep software current, remove applications that no longer serve a purpose, and take end-of-support notices seriously; for the industry, safe retirement must become part of product design.